CAMLIS · November 14, 2025

Adversarial ML Attacks on Financial Reporting via Maximum Violated Multi-Objective Attack

Adversarial ML Attacks on Financial Reporting via Maximum Violated Multi-Objective Attack video thumbnail
Why it matters

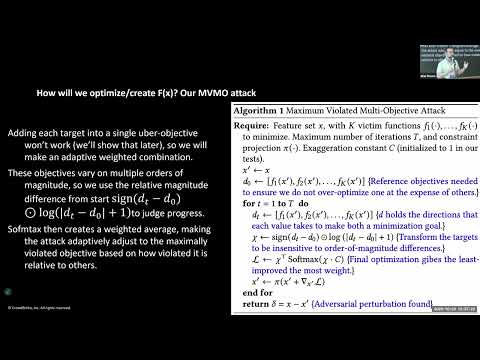
Edward Raff and collaborators introduce Maximum Violated Multi-Objective attacks for manipulating financial statements while simultaneously reducing model-generated fraud scores. Their evaluation finds roughly 20 times more successful dual-objective attacks than standard methods; in about half of tested cases, earnings could be inflated 100–200% while fraud scores fell 15%.

My takeaway: Red-team financial models against realistic combinations of attacker goals instead of optimizing one metric at a time. Validate model outputs against accounting constraints and source evidence, monitor coordinated feature shifts, and retain independent audit controls rather than treating a low fraud score as assurance.
Keep exploring

More curated notes connected through AI Red Teaming and Agent Security.

OpenAI News · framework

Pacing model development in an era of cyber-critical capabilities

OpenAI says preliminary evidence that Astra may meet its Critical cybersecurity threshold led it to pause frontier reinforcement-learning work for two weeks and keep its largest planned run on hold. New safeguards include stronger workload and network isolation, continuous boundary testing, token-level monitoring that escalates suspicious tool activity, and broader alignment checks for deception, reward hacking, and unauthorized access.

OpenAI News · framework

A blueprint for democratic governance of frontier AI

OpenAI proposes a three-part U.S. frontier-AI governance model: harmonize emerging state safety laws into a federal baseline, strengthen CAISI as an evaluation and standards institution, and coordinate a broader resilience program. Proposed controls include severe-risk evaluations, transparency reports, independent audits, safety-incident reporting, model-weight security, whistleblower protection, and periodic technical assessments.

OpenAI News · framework

OpenAI’s Frontier Governance Framework

OpenAI's 22-page Frontier Governance Framework maps its frontier-model processes to California's Transparency in Frontier AI Act and the EU AI Act's general-purpose AI code. It documents lifecycle risk assessment, cyber-offense and other risk tiers, mitigation and residual-risk decisions, critical-incident handling, security risk management, model reporting, external review, responsibility allocation, and change control.